Rabbit’s R1 AI gadget is embroiled in another controversy, this time due to a severe security flaw. A group called Rabbitude discovered hardcoded API keys in Rabbit’s codebase, compromising sensitive data. These keys allowed unauthorized access to Rabbit’s accounts with third-party services, including ElevenLabs and SendGrid, potentially exposing all responses generated by R1 devices. Despite Rabbitude notifying Rabbit over a month ago, the company was slow to act, only recently revoking most of the keys. However, Rabbitude still had access to the SendGrid key as of today. Rabbit’s spokesperson, Ryan Fenwick, stated that the company is investigating the issue but has not found any critical system compromises or customer data breaches yet. The R1’s launch, marred by poor battery life, limited features, and error-prone AI, already tarnished its reputation. This security lapse severely undermines public trust, putting Rabbit in a precarious position.
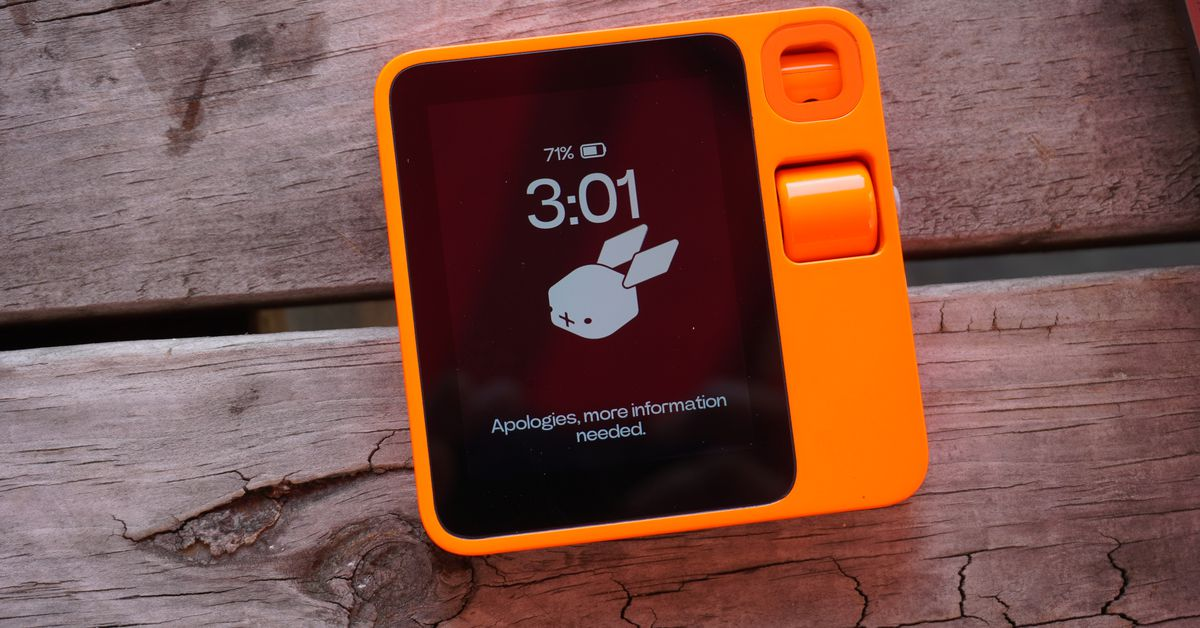
Rabbit’s R1 AI Gadget Faces Major Security Breach, Trust Eroding Fast
Rabbit’s R1 AI gadget is facing a serious security breach, risking sensitive data.
1–2 minutes

TOP STORIES

CERT-In reported that AI agents accessed sensitive data in Indian organizations during testing phases …

Flock’s gunshot detection technology faces backlash amid privacy concerns …

OpenAI has alerted the FBI after an employee allegedly planted a hidden recording device in an executive conference room …

Character.AI’s bankruptcy filing reveals the challenges of scaling AI products …

Meta’s new Muse Wonder models promise enhanced capabilities and memory retention for personal AI assistants …

Apple is tightening privacy controls on macOS to protect users from AI risks …